

Security assessments
that tell you
what to fix first.
Independent architecture reviews, firewall assessments and vulnerability remediation for networks, firewalls and cloud, with findings your team can act on.
what we offer
Security Assessments
We don’t offer a checkbox audit and a PDF report. We engage at the architecture level, understanding your environment, your constraints, and your risk profile, and deliver outcomes that hold up in the real world.
Where we work
Our assessments cover network and firewall estates, cloud network configuration and industrial environments, in regulated manufacturing, pharmaceutical GxP plants, logistics and European institutions.
The common thread is complexity. These aren’t environments where a standard methodology is enough.
Architecture Review
Independent review of your network and security architecture against your risks and current good practice
Zero Trust Gap Assessment
Where your segmentation and access model stands today against Zero Trust principles, and what to change first
Firewall Architecture & Remediation
Design, assessment, and optimisation across Palo Alto, Check Point, and Cisco environments
Vulnerability Assessment
Risk-based assessments in regulated and GxP environments, with prioritised remediation plans
Configuration Hardening
Firewalls, network devices and cloud configuration checked against CIS benchmarks and vendor best practice
Security Governance & Compliance
NIST, ISO 27001, and IEC 62443 alignment, policy development, gap analysis, and audit readiness
What we deliver
Every engagement is scoped to your environment and delivered by a senior practitioner with direct sector experience.
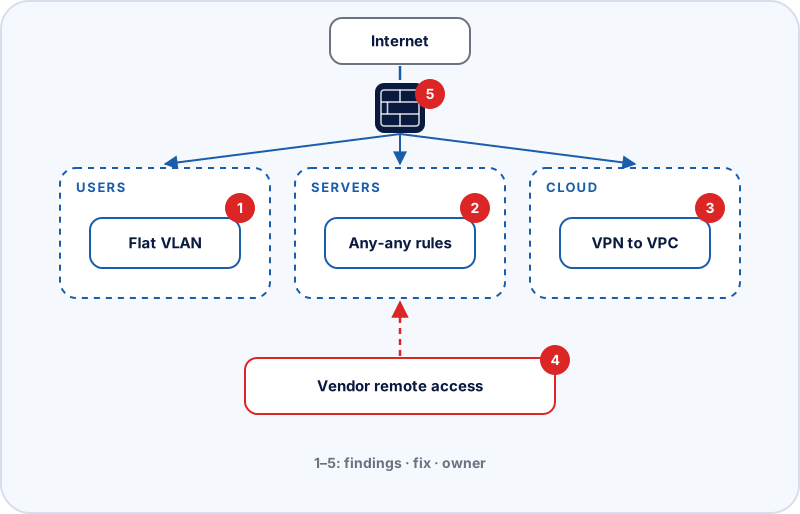
1. Architecture Review
An independent review of your network and security architecture: segmentation, firewall placement, remote access and cloud connectivity, measured against your risks, Zero Trust principles and the frameworks you answer to.
- Design and configuration review
- Risk-ranked findings with business context
- Target architecture and phased roadmap
2. Vulnerability Assessment & Remediation
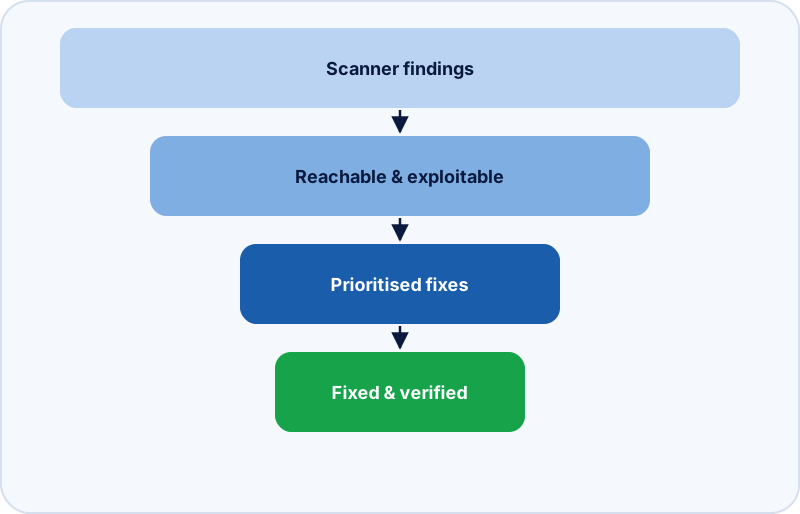
We run and interpret vulnerability scans with Qualys or Nessus, prioritise by real exposure in your environment, help your teams fix what matters and verify the fixes. Application penetration testing is delivered with trusted partners when needed.
- Scanning and triage
- Remediation planning with owners and deadlines
- Verification after fixes
3. Firewall Architecture & Remediation
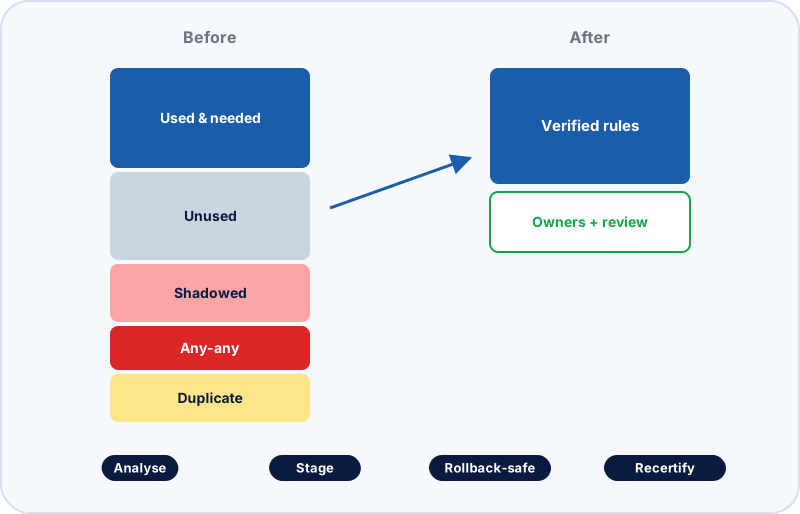
Comprehensive firewall security assessments, rule-set review, and policy optimisation across Palo Alto, Check Point, and Cisco environments, with structured, prioritised remediation plans that are executable, not just advisory.
- Rule-set review, clean-up, and policy optimisation
- Prioritised remediation plans across Palo Alto, Check Point, and Cisco
- Structured assessment with actionable, executable output
Why Choose BlueCyber?
Practitioner-led, not consultant-led
Every engagement is run by a senior architect with hands-on delivery experience in the environment type you operate in
Regulated sector depth
Deep experience in pharmaceutical GxP, regulated manufacturing, automotive, and European institutional environments
Framework-aligned delivery
NIST SP 800-82, IEC 62443, ISO 27001, and NIST CSF, applied practically, not decoratively
EU-based, internationally experienced
Based in Czechia and Romania, with engagements delivered across the EU and the UK
Bring us your hardest security problem.
If your environment is complex, regulated, or simply unusual, that’s where we work best.
We start with an honest assessment, and we don’t oversell what we find.
Book an architecture review