

OT/ICS Security Architecture
for environments where
downtime is not an option.
Practitioner-led industrial cybersecurity, from asset discovery and network segmentation through to IEC 62443 and NIST 800-82 aligned hardening programmes.
OT/ICS Security
Industrial Security Architecture
Operational technology environments carry unique risk: legacy systems, proprietary protocols, safety-critical processes, and convergence with IT networks. We bring deep, hands-on OT security experience, not generic IT security applied to industrial settings.
The challenge
Most organisations know their OT environment is exposed. They just don't know where to start, or who to trust to work in environments where an incorrect firewall rule can stop a production line.
NIS2 deadlines are approaching. IEC 62443 compliance is becoming a procurement requirement. And the gap between IT security teams and OT engineers isn't closing on its own.
Unsegmented OT networks
Flat networks where a compromise in IT can reach PLCs, HMIs, and safety systems within minutes
No visibility into OT assets
Unknown devices, undocumented communication flows, and legacy systems that predate the cybersecurity function
Regulatory pressure mounting
NIS2, IEC 62443, and sector-specific requirements demanding documented security programmes and evidence of controls
IT/OT convergence risk
Cloud connectivity, remote access, and digital transformation initiatives expanding the OT attack surface
Vendor dependency
Reliance on OEM remote access, unpatched systems, and third-party maintenance windows that bypass security controls
Safety-critical constraints
Environments where security changes require careful coordination with production, safety systems, and plant operations
OT Security Architecture Assessment
Our flagship engagement, a structured, practitioner-led assessment of your OT/ICS environment that delivers a clear security roadmap with prioritised, actionable recommendations.
1. Discovery & Baseline
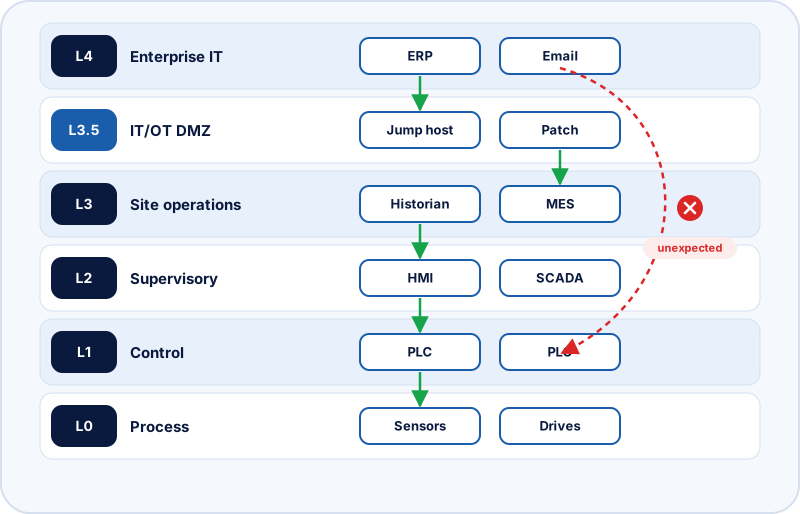
We map your OT environment, assets, communication flows, network topology, and trust boundaries, to establish the security baseline. No scanning tools pointed blindly at production networks. We work with plant engineers, review configurations, and build the picture methodically.
- OT/ICS asset inventory with device classification
- Communication flow analysis and dependency mapping
- Network architecture documentation (Purdue model alignment)
2. Risk Assessment & Gap Analysis
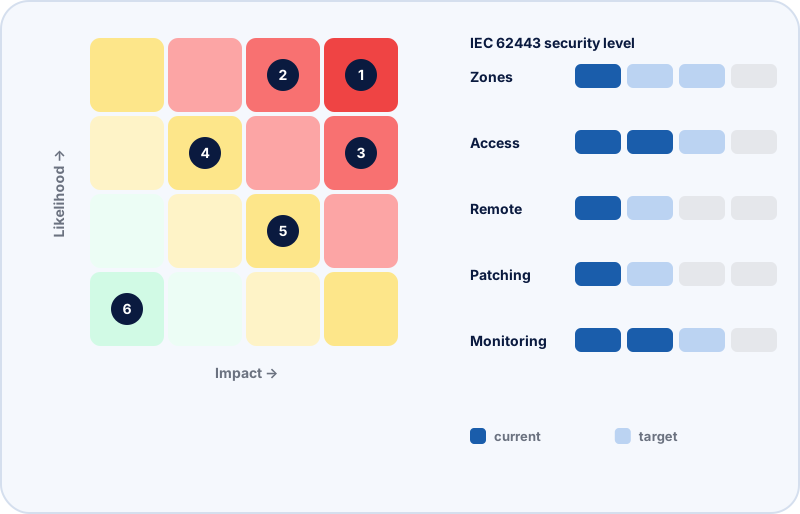
We evaluate your current security posture against IEC 62443 and NIST SP 800-82 requirements, identifying gaps with real-world risk context, not theoretical vulnerability scores, but actual exposure in your specific operational environment.
- IEC 62443 / NIST SP 800-82 gap analysis
- Risk-prioritised findings with business impact context
- NIS2 readiness assessment for OT-specific requirements
3. Segmentation Design & Roadmap
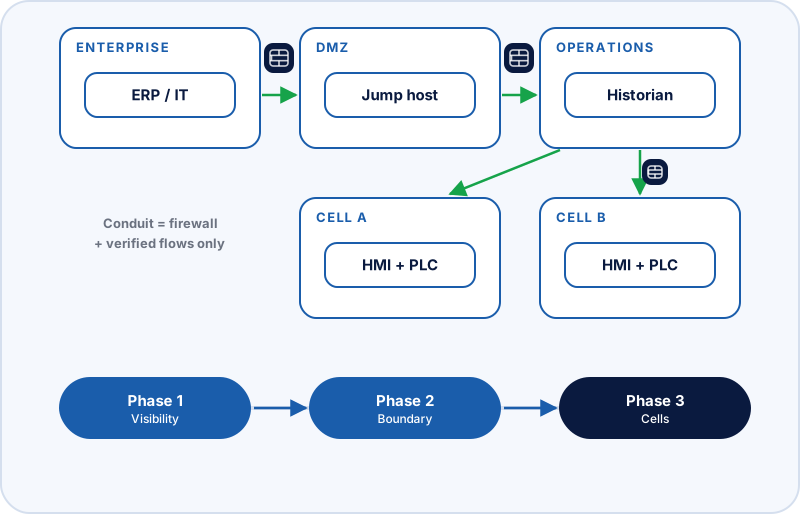
We design the target network architecture, zones, conduits, firewall policies, and access controls, and deliver a phased implementation roadmap that respects production schedules, change windows, and organisational capacity.
- Zone and conduit design (IEC 62443-3-2 aligned)
- Firewall policy design for IT/OT boundary and internal segmentation
- Phased implementation roadmap with production-safe milestones
Beyond the assessment
Assessment is the starting point. We also deliver hands-on implementation, ongoing governance, and fractional CISO support for organisations that want a long-term security partner.
Segmentation Implementation
Hands-on deployment of network segmentation, firewall policies, and access controls, working alongside your plant engineers and OT vendors.
Ongoing OT Security Governance
Quarterly reviews, policy updates, incident response readiness, and continuous improvement of your OT security programme.
Security Architect on Retainer
Senior security architecture on a retained basis: design reviews, change and firewall policy approvals, vendor and project support, and a quarterly review with management, without a full-time hire.
NIS2 Compliance Integration
Extend your OT security programme to meet NIS2 requirements, incident reporting, supply chain security, and management accountability.
Why BlueCyber for OT security
Hands-on OT experience
We've configured Palo Alto firewalls in pharmaceutical GxP environments, segmented SCADA networks in manufacturing plants, and coordinated security changes with OT vendors who don't speak "cybersecurity."
Production-safe methodology
We don't scan production networks without coordination. We don't deploy untested rules during production hours. We understand that in OT, availability and safety come first.
Framework-aligned, not framework-decorative
IEC 62443, NIST SP 800-82, and NIS2 applied to your specific environment, not a generic mapping exercise that ticks boxes but doesn't reduce risk.
EU-based, GDPR-compliant
Based in Czechia and Romania, with engagements delivered across the EU and the UK. Client configurations are handled under NDA and stay in the EU.
How to start
Fixed-scope engagements
Scope, duration and deliverables for every engagement are on one page, so you know what you are buying before the first call.
Ready to secure your OT environment?
Start with a free consultation. We'll discuss your environment, your concerns, and whether our OT Security Architecture Assessment is the right fit.
No sales pitch. No generic proposals. Just an honest conversation about your OT security posture.
Book an OT security consultation