

NIS2 is now national law. Here is what it asks of your network.
Czech Act 264/2025 and Romanian OUG 155/2024 turn NIS2 into concrete obligations with deadlines. We check your network, cloud and OT controls against them and tell you plainly what an auditor would flag.
Compliance & Governance
Compliance that holds up to a technical audit
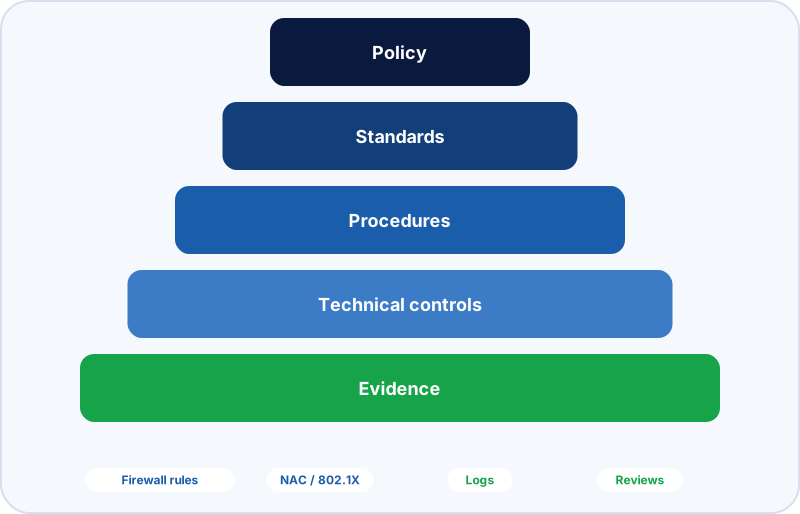
Most regulated companies have a policy folder. Fewer can show an auditor that segmentation, access control, logging, remote access and backup actually work. We come from security architecture, so we check the controls themselves, not only the documents that describe them.
What applies to you
Czechia and Romania have both transposed NIS2. Registration deadlines have passed, enforcement has started, and the obligation to have security measures in place is tied to a date on your registration decision.
The technical measures are where most companies are weakest, because they need network and OT engineering, not another document.
Czech Act No. 264/2025 Coll.
In force since 1 November 2025. Regulated services register with NÚKIB and fall under the higher or lower obligations regime (Decrees 409/2025 and 410/2025). Security measures and incident reporting apply no later than one year after the registration decision is delivered.
Romanian OUG 155/2024 and Law 124/2025
Essential and important entities register with DNSC, then follow a sequence: classification decision, risk level assessment within 60 days, annual maturity self-assessment, remediation plan, and audits by DNSC-certified auditors. First sanction proceedings started in 2026.
NIS2 Directive (EU) 2022/2555
The common baseline: risk management measures under Article 21, supply chain security, management liability, and incident reporting within 24 hours, 72 hours and one month.
DORA
For financial entities: ICT risk management, incident reporting, third-party oversight and resilience testing, in force since January 2025.
ISO/IEC 27001:2022
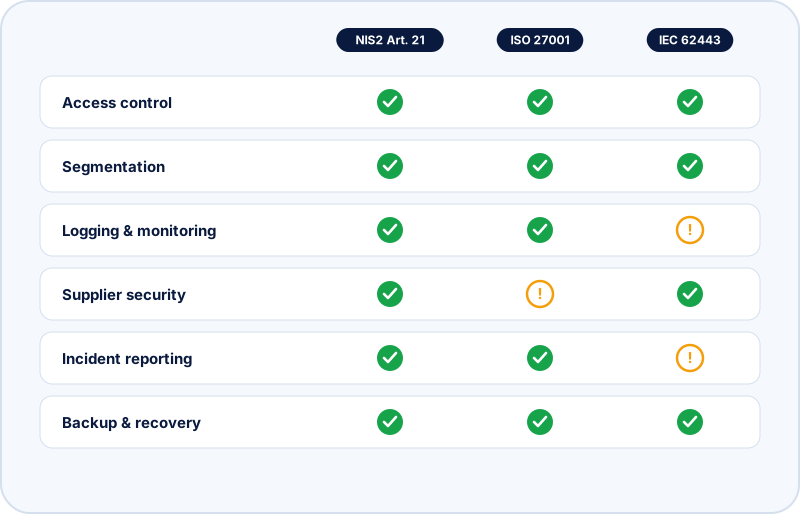
The management system standard most of our clients certify against. A NIS2 technical check covers much of Annex A network, access and operations controls.
IEC 62443
Industrial automation and control systems security. The zone and conduit model is how we translate NIS2 network requirements into a plant.
NIS2 Technical Measures Check: what happens in two weeks
A fixed-scope engagement for companies that have registered and now need to know where their technical controls stand. It prepares you for the audit; it is not the formal audit itself.
1. Scope and regime
We confirm which regime you fall under (Czech higher or lower obligations, Romanian essential or important), which systems support the regulated service, and the date your deadline runs from.
- Regime and scope confirmed in writing
- Systems and sites in scope listed
- Deadline and reporting duties mapped
2. Technical measures review
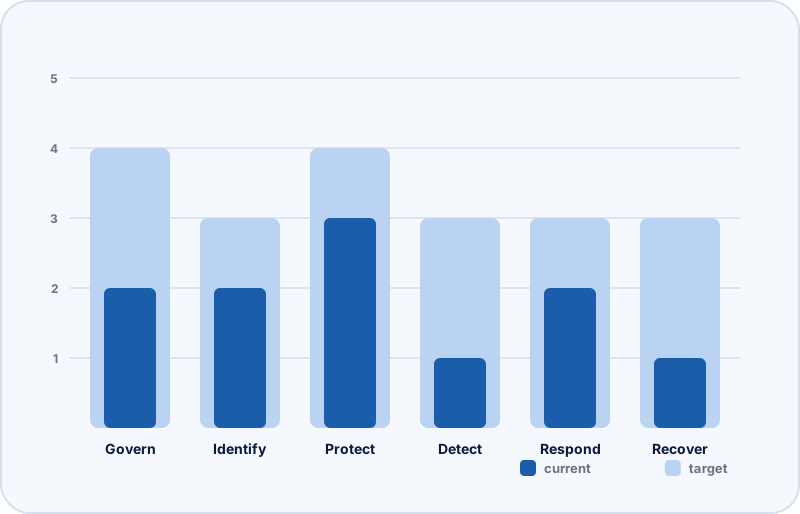
We review the controls the decrees and DNSC orders expect: network segmentation, access control and MFA, logging and monitoring, remote and vendor access, backup and recovery. On site where production networks are involved.
- Gap list against the technical measures
- Evidence of what already meets them
- Findings ranked by risk, with the auditor view
3. Fix plan and handover
You receive a prioritised plan with owners, effort and sequencing, written so your team or integrator can execute it. We walk it through with management and stay available for questions.
- Prioritised fix plan
- Management summary
- Findings walkthrough with your team
After the check
Compliance is a programme, not a project. These are the services clients take once the first gaps are closed.
Security Architect on Retainer
Senior security architecture on a retained basis: design reviews, change and firewall policy approvals, vendor and project support, and a quarterly review with management, without a full-time hire.
Technical control reviews
Periodic reviews of firewall, segmentation and access controls that produce the technical evidence auditors ask for, ready before the audit rather than assembled during it.
Supply chain risk assessment
Vendor tiering, evidence-based questionnaires and ongoing monitoring, a NIS2 and DORA requirement that most companies have not yet formalised. Our vendor security whitepaper covers the method.
ISO 27001 and DORA support
Gap analysis, control implementation and audit preparation when your programme goes beyond NIS2.
Why BlueCyber for NIS2
Technical depth behind governance
We come from hands-on security architecture, so the controls we check and design are technically correct and practical to implement.
Local law, read in the original
We work with the Czech act and decrees and the Romanian ordinance and DNSC orders directly, in Czech and Romanian, not from a summary.
Multi-framework
NIS2, ISO 27001, DORA and IEC 62443 overlap heavily. One programme of evidence serves all of them.
Based in the EU, delivering in CZ and RO
BlueCyber s.r.o. in Czechia and BlueCyber Solutions SRL in Romania, in English, Czech or Romanian.
How to start
Fixed-scope engagements
Scope, duration and deliverables for every engagement are on one page, so you know what you are buying before the first call.
Not sure which regime you are in, or when your deadline is?
Start with a free 30-minute call. We will confirm your regime, your deadline and what the check would cover in your environment.
No pressure. No generic proposals. Just clarity on your next steps.
Book a 30-minute scoping call